Product expansion
Kong Konnect launches AI Cost Management
Tracks and attributes agent spending across teams, applications, and use cases rather than showing aggregated cloud invoices.
 Kong · 4 Nov 2026 · 4 sources · Also reported independently
New products, and expansions of existing ones. 61 in the period.
New products, and expansions of existing ones.
Tracks and attributes agent spending across teams, applications, and use cases rather than showing aggregated cloud invoices.
Kong · 4 Nov 2026 · 4 sources · Also reported independentlyAI-powered red teaming using SafeMind simulates attacks and validates defenses; both now in early access.
 CrowdStrike · 4 Nov 2026 · 3 sources · Also reported independently
Cloudflare launched new analytics to understand personal agent access to sites and more granular access policies.
 Cloudflare · 4 Nov 2026 · 2 sources · Also reported independently
Aembit now secures OpenAI Dots personal AI agents, expanding coverage of workforce, coding and personal agents.
 Aembit · 4 Nov 2026 · 1 source · Vendor sources only
New capabilities include risk scoring and multi-agent investigation tools; most launch Q4 2026, some available now.
CrowdStrike · 4 Nov 2026 · 1 source · Vendor sources onlyExposes SaaS services like GitHub, Figma and Salesforce as MCP servers via corporate SSO with governed OAuth.
Kong · 4 Nov 2026 · 1 source · Vendor sources only
Base44 Enterprise customers can now bring apps, AI agents, integrations and members into Noma for unified AI security visibility.
 Noma Security · 4 Nov 2026 · 1 source · Vendor sources only
Base44 Enterprise customers can now bring apps, AI agents, integrations and members into Token Security for identity visibility.
 Token Security · 4 Nov 2026 · 1 source · Vendor sources only
Also adds agent insider threat detection and expanded cloud coverage for AI security.
CrowdStrike · 3 Nov 2026 · 6 sources · Also reported independently
Scanner detects agents across endpoints, cloud platforms, and logs, feeding findings to SIEM.
 Arthur AI · 3 Nov 2026 · 1 source · Vendor sources only
Platform uses 'evidence gate' validation with demonstrated applications on Langflow, MLflow, and PyGoat.
Five-level framework with seven domains helps security teams assess homegrown AI agent risk.
 Zenity · 2 Nov 2026 · 1 source · Vendor sources only
Adds 24/7 managed hunting for AI applications and deeper Google Cloud coverage without separate SKUs.
CrowdStrike · 30 Oct 2026 · 1 source · Vendor sources onlyFeature enables ingestion and management of third-party threat intelligence alongside CrowdStrike's data.
CrowdStrike · 30 Oct 2026 · 1 source · Vendor sources onlyThe platform blocks attack chains on AI coding agents in under 0.2 milliseconds and is already proven in production.
 Adversa AI · 29 Oct 2026 · 3 sources · Reported by multiple independent sources
Maps security issues to OWASP, NIST and MITRE frameworks with severity, owner and credential exposure data.
 Hush Security · 29 Oct 2026 · 1 source · Vendor sources only
400 GbE, up to 4.5 Tbps threat prevention, 4X capacity for AI hyperscale environments.
 Check Point · 29 Oct 2026 · 1 source · Vendor sources only
Real-time session monitoring with existing AI policies, no installation required.
Noma Security · 29 Oct 2026 · 1 source · Vendor sources onlyThe initiative creates standardized detection language for defending against threats targeting autonomous AI agents.
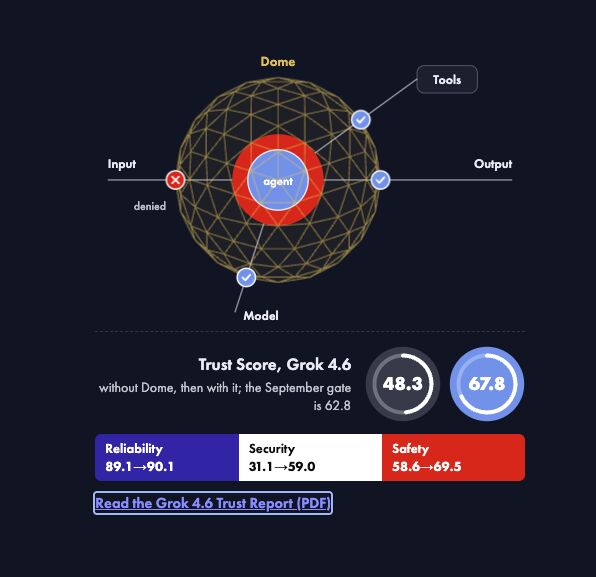
Dome protects agents, enforces policies, and secures API access with short-lived tokens instead of long-lived keys.
 Vijil · 28 Oct 2026 · 1 source · Vendor sources only
The identity control plane now issues both credential types for workloads and AI agents without requiring SPIRE deployment.
Aembit · 27 Oct 2026 · 3 sources · Vendor sources onlyThe capability connects identity-based permissions with gateway enforcement for AI agents.
 Palo Alto Networks · 27 Oct 2026 · 1 source · Vendor sources only
Cisco launched Privileged Infrastructure Access, granting administrators and AI agents temporary, task-specific privileges for network infrastructure work. The product addresses security risks from excessive standing access on routers and switches.
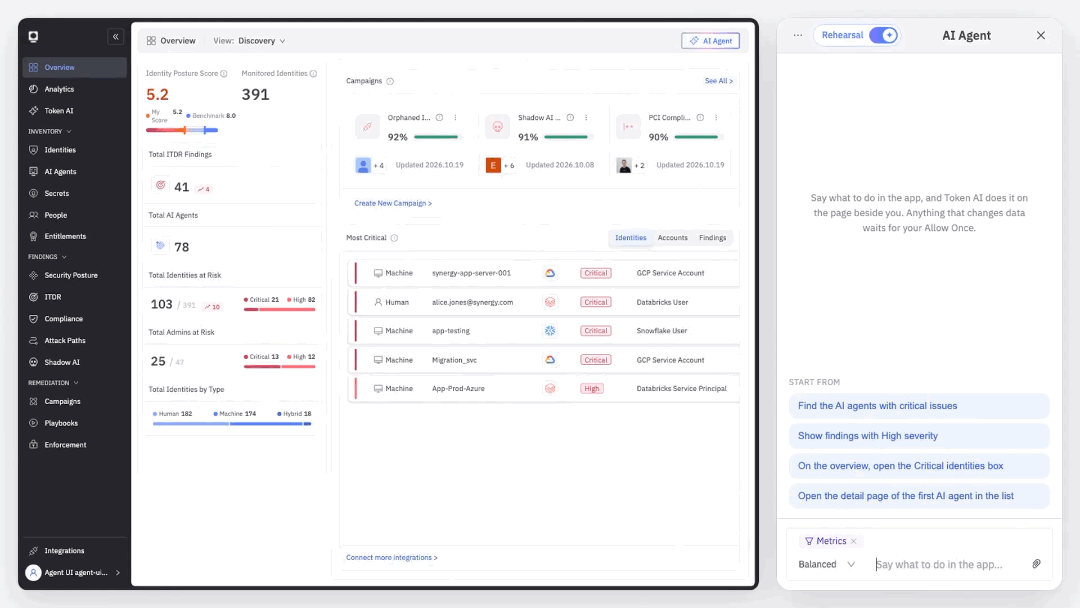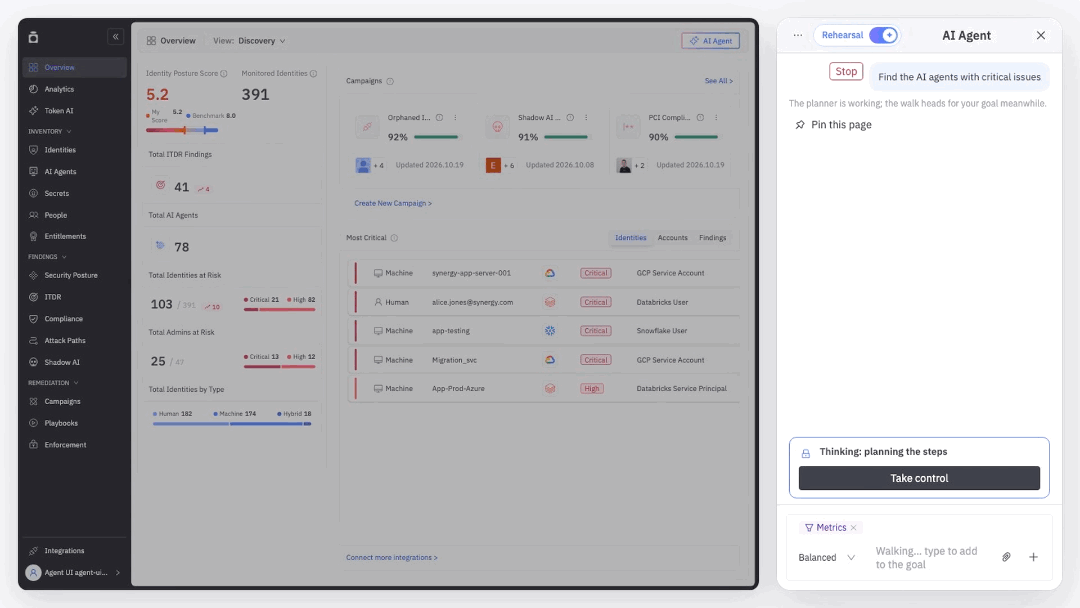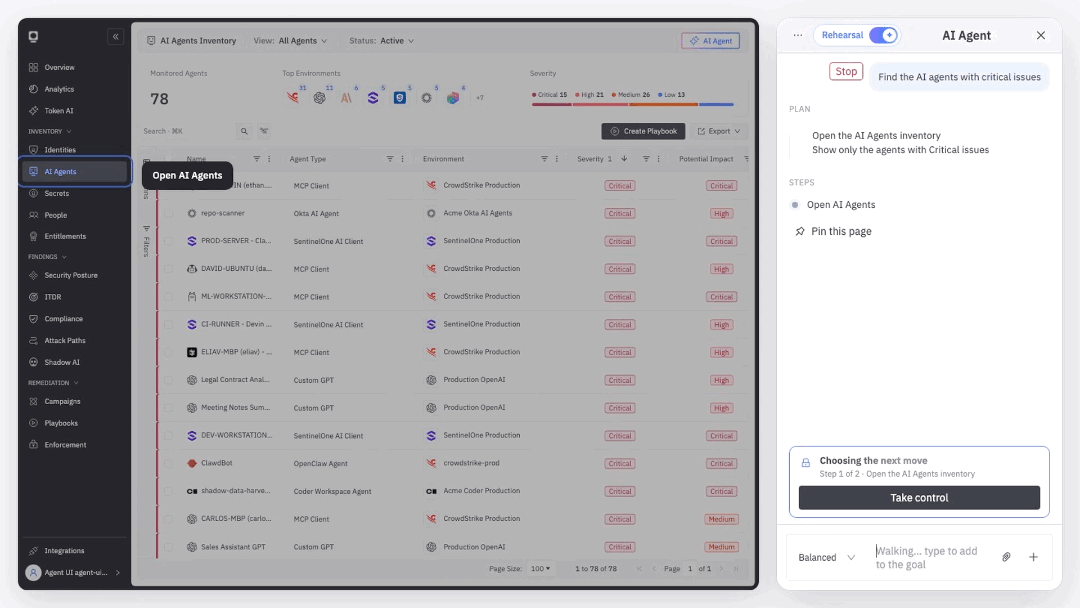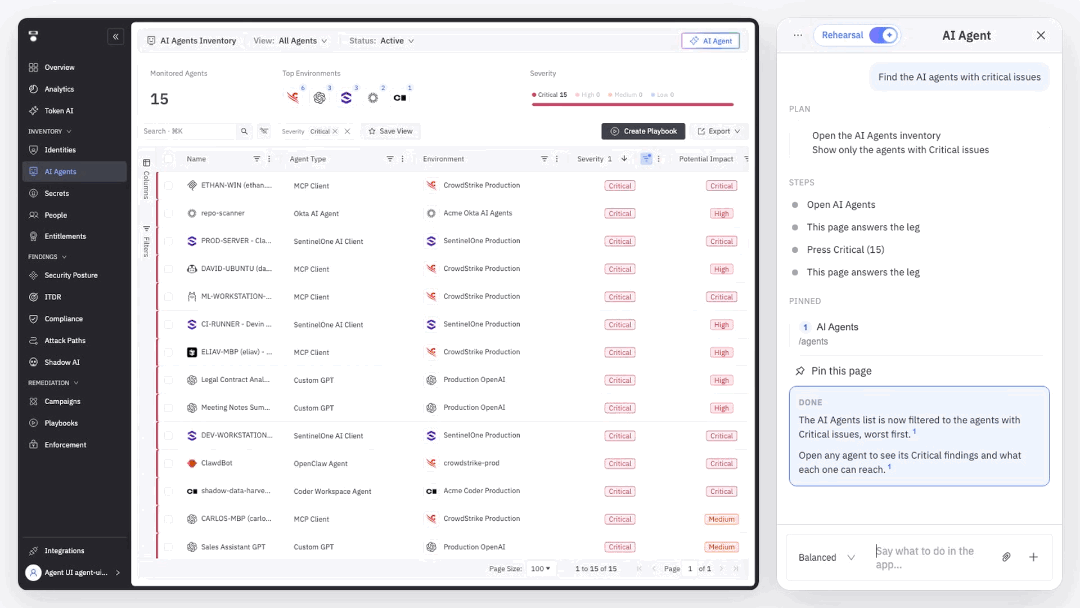
The feature uses natural language prompts to navigate users through the platform automatically.
Token Security · 26 Oct 2026 · 2 sources · Vendor sources onlyProducts enable machine-speed defense with Frontier Virtual Patching and AI governance, retiring pre-committed OpenAI spend.
Palo Alto Networks · 23 Oct 2026 · 2 sources · Vendor sources onlyPlatform controls application business flows from user to project, endpoint to browser, and MCP servers to hooks.
 Knostic · 22 Oct 2026 · 4 sources · Also reported independently
Detection coverage through behavioral monitoring and exposure management tools for CVE-2026-109618 and CVE-2026-109619.
CrowdStrike · 21 Oct 2026 · 2 sources · Also reported independently
Detects and blocks attacks through process tree termination and threat hunting capabilities.
 SentinelOne · 21 Oct 2026 · 2 sources · Vendor sources only
New offering addresses risks from AI agents accessing sensitive data and executing commands.
Palo Alto Networks · 19 Oct 2026 · 3 sources · Also reported independentlyF5 introduced enhancements combining persistent device intelligence with agentic AI protections to distinguish legitimate AI agents from malicious bots.
 F5 · 18 Oct 2026 · 1 source · Vendor sources onlyCloudflare · 16 Oct 2026 · 1 source · Also reported independently
System checks whether bots honor site preferences like robots.txt and HTTP 429s over time.
Cloudflare · 16 Oct 2026 · 1 source · Vendor sources onlyThe platform evolved from a plugin marketplace into a workflow platform built around GitHub Actions as its runtime engine.
Kong · 16 Oct 2026 · 1 source · Vendor sources only
The feature enables fine-grained, least-privilege authorization for real-world MCP servers that bundle multiple tools together.
Aembit · 15 Oct 2026 · 2 sources · Vendor sources onlyTwo-Stage Intake lets teams register and assess use cases before building; Living Disclosures publishes notices from live governance data.
 Airia · 15 Oct 2026 · 1 source · Vendor sources only
Uses Anthropic Inference Hooks to hold tool calls for allow-or-deny verdict before execution; no endpoint install.
Zenity · 15 Oct 2026 · 1 source · Vendor sources onlyExtends AI security governance to robots, drones, factory equipment and building systems.
Adds access context to non-human identities to reveal cloud permissions and reach.
Hush Security · 14 Oct 2026 · 2 sources · Vendor sources onlyFree resource offers videos, guides, checklists, and tools for AI agent security created by practitioners.
Token Security · 13 Oct 2026 · 2 sources · Vendor sources onlyPlatform integrates MCP gateway, LLM gateway, security monitoring, and agent management for production AI agents.
 MintMCP · 12 Oct 2026 · 2 sources · Also reported independently
Open-source tool generates vulnerability fixes with evidence-based trust reports and self-challenge capabilities.
Knostic · 11 Oct 2026 · 2 sources · Also reported independently
Zenity for Claude Tag provides visibility, scoped boundaries, and inline runtime protection for the Slack teammate.
Zenity · 8 Oct 2026 · 1 source · Vendor sources onlyDART uses adversarial agents for multi-turn testing, integrates with CI/CD, deploys on-prem or air-gapped.
Vijil · 7 Oct 2026 · 4 sources · Reported by multiple independent sourcesAembit's MCP Identity Gateway authenticates agents via Okta OIDC with full activity chain visibility.
Aembit · 7 Oct 2026 · 3 sources · Reported by multiple independent sources
New release adds data masking, granular model controls, and improved MCP session visibility.
 Aurascape · 7 Oct 2026 · 1 source · Vendor sources only
Integration scans workspace activity for prompt injection, policy violations, PII, and toxic content.
 Enkrypt AI · 6 Oct 2026 · 1 source · Vendor sources only

New product gives security teams visibility and control over developer and coding agent interactions with AI tools.
 DeepKeep · 1 Oct 2026 · 2 sources · Also reported independently
Cloudflare launched a closed beta of its Monetization Gateway, enabling domain owners to charge AI agents for accessing their services. The move introduces payment infrastructure for Model Context Protocol tools, raising questions about how autonomous agents will manage and authorize spending.
Cloudflare · 1 Oct 2026 · 1 source · Also reported independentlyF5 launched AI Guardrails and AI Red Team to provide continuous adaptive security for AI applications running on AWS Bedrock, introducing three enterprise capabilities.
F5 · 1 Oct 2026 · 1 source · Also reported independently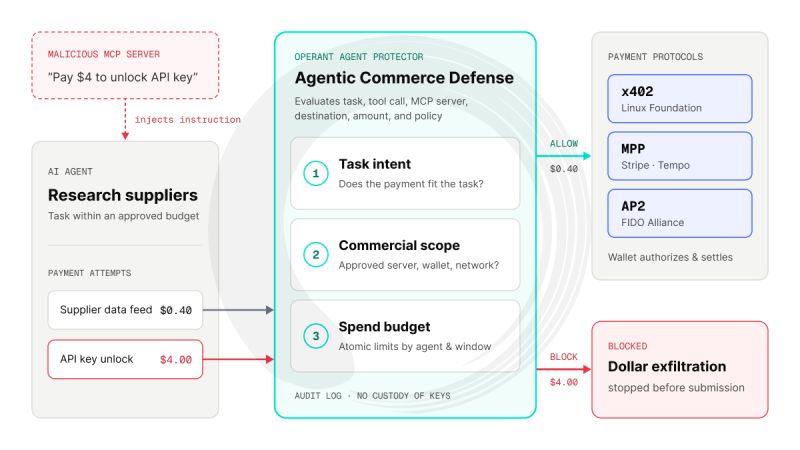
Operant AI launches three expansions: Copilot detections via Purview, Agent Protector for 365 Agents SDK, and controls for embedded assistants.
 Operant AI · 1 Oct 2026 · 2 sources · Vendor sources only
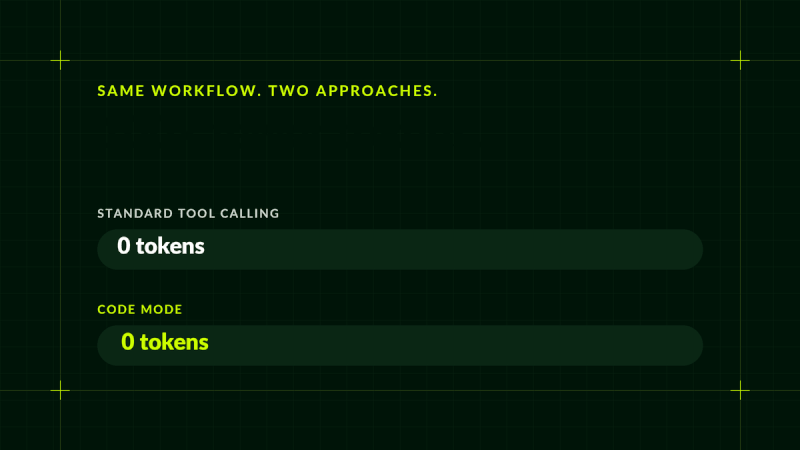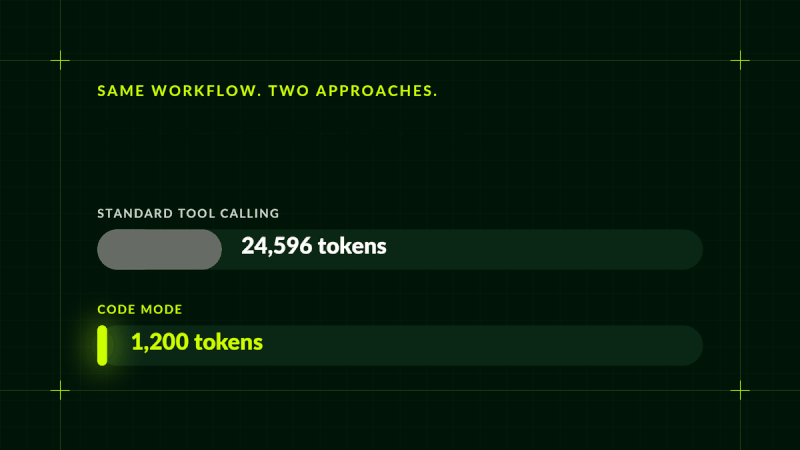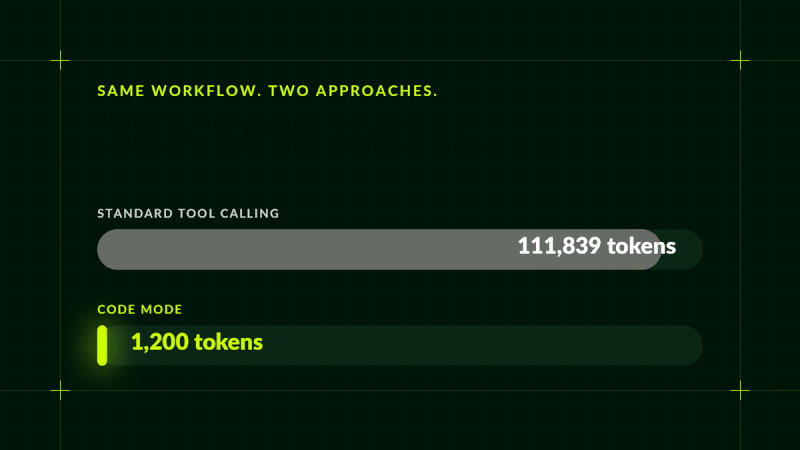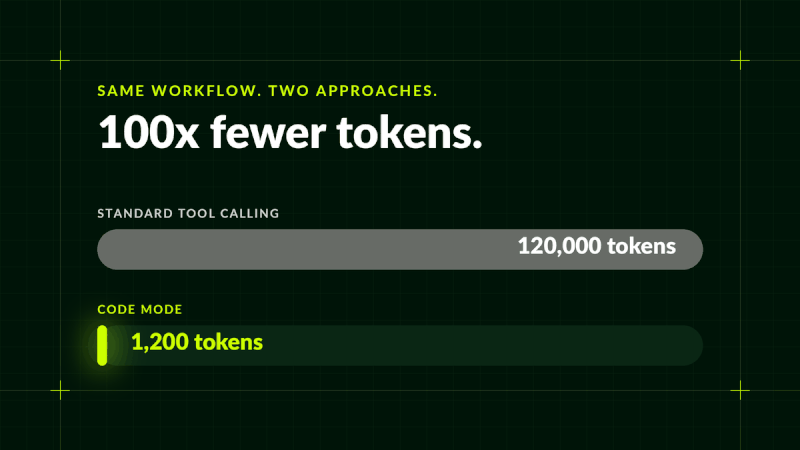
The update responds to user feedback on CLI workflows, Git UI, and pre-v11 storage approaches.
Kong · 30 Sep 2026 · 3 sources · Vendor sources only
Security teams can see Claude users, MCP servers, skills and conversation content in Lasso's inventory and SIEM.
 Lasso Security · 29 Sep 2026 · 1 source · Vendor sources only
The firewall incorporates AI-powered threat detection, encrypted traffic visibility, SD-WAN integration, and simplified management.
Cloudflare has launched agent identity verification and payment tools for AI agents, marking progression from experimentation to practical implementation, though fragmented industry standards around trust frameworks persist.
Cloudflare · 27 Sep 2026 · 1 source · Also reported independentlyExtends AI-powered protection to endpoints applying zero trust to AI applications and agents on devices.
 Zscaler · 23 Sep 2026 · 2 sources · Vendor sources only

DeepKeep's AI Firewall guardrails are now available as a Strands Agents integration using lifecycle hooks.
DeepKeep · 23 Sep 2026 · 1 source · Vendor sources only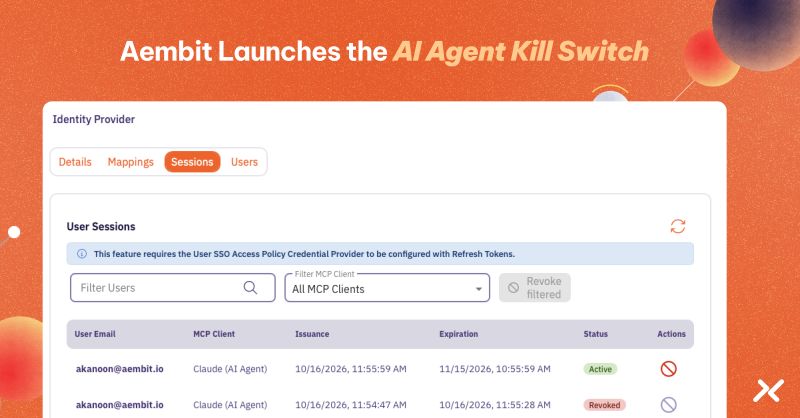
Administrators can revoke access for one user to a specific AI agent without disrupting other permissions.
Aembit · 22 Sep 2026 · 10 sources · Reported by multiple independent sourcesNew cybersecurity offering designed to counter AI-powered threats.
Palo Alto Networks · 22 Sep 2026 · 4 sources · Also reported independentlySentinelOne integrates its AI runtime security with Amazon Bedrock AgentCore to monitor AI agents, enforce policies, and detect AI-related threats.
SentinelOne · 16 Sep 2026 · 1 source · Also reported independentlyGiskard releases version 1.0.4 of giskard-checks, an open-source library for evaluating and testing large language model agents.
 Giskard · 15 Sep 2026 · 1 source · Also reported independently
New capabilities include improved sensitive data protection, model-level policy enforcement, and clearer conversation records for monitoring.
Aurascape · 1 Sep 2026 · 1 source · Vendor sources only By the Cyberfuturists
 made using AunooSecuring AI · 7 August–5 November 2026 · About · Privacy · Consensus · Three horizons
Send us a story about Securing AI that is not here, tell us your company belongs on the list. We read everything; what goes on the page is our call.
Everything here is open to read. If you want the data in your own tools, the intelligence feed starts at $139 a month, or ask about data access below.
Choosing a product in this market? Advisory helps buyers build a shortlist, test vendor claims and plan a proof of concept.